


Cybersecurity incident affected 48 mosques, four madrasahs; no ransom paid: MUIS
The incident, which was first reported earlier in the week, involved a human resources and payroll system.
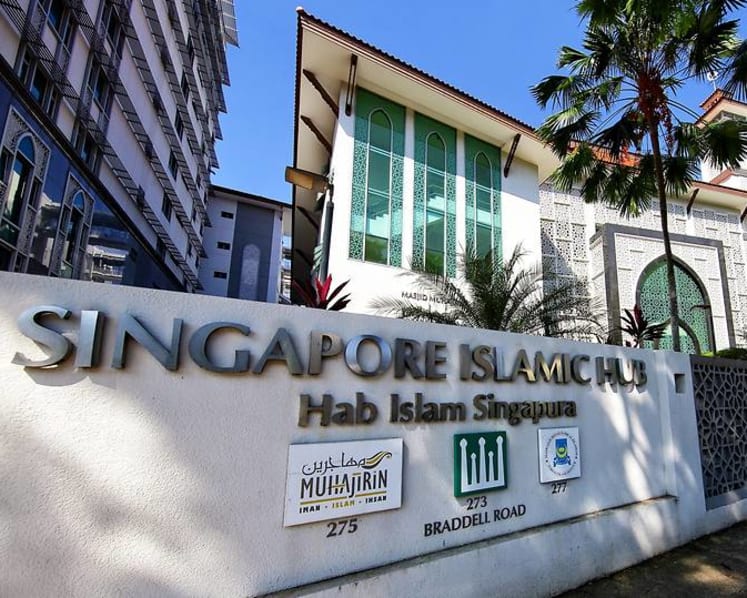
Exterior of the Islamic Religious Council of Singapore (MUIS) building. (Photo: Majlis Ugama Islam Singapura)

This audio is generated by an AI tool.

SINGAPORE: No ransom was paid following a cybersecurity incident involving software vendor Avelogic, the Islamic Religious Council of Singapore (MUIS) said on Thursday (Sep 17).
The incident, first reported on Tuesday, affected Avelogic's human resources and payroll system and clients across different sectors. In the community sector, this included 48 mosques, four madrasahs, the Islamic Learning Hub and Management Office and Mosque-Madrasah-Wakaf Shared Services, MUIS said.
A police report was made, and Avelogic is continuing to investigate the incident and its wider impact, MUIS said.
The council added that it was “concerned” about the impact on the affected organisations and their employees and that it was working with those affected to ensure salaries would continue to be paid on time.
"Alternative payroll arrangements are already in place, and there has been no disruption to religious or public-facing services," said MUIS.
Avelogic has since recovered the affected data and engaged independent cybersecurity experts to investigate the incident.
Based on investigations so far, there is no evidence that a large amount of data was taken from the system, MUIS said. Data stored in the affected system is also encrypted as an additional layer of protection.
Investigations and security checks are ongoing, and the system will only resume operations after the relevant safeguards and checks have been completed.
"MUIS will continue to support the affected community sector organisations to ensure essential HR and payroll functions continue without disruption," the council said.
MUIS told CNA on Tuesday that the incident did not affect the delivery of public-facing or government services. It did not reveal the number of people affected or what information may have been compromised.
Separately, Avelogic published a cybersecurity incident notice concerning its SmartHRMS system, which it described as a payroll and human resources management system for enterprises.
In an update on Monday, the company said an independent forensic investigation found no evidence of bulk data exfiltration, based on available Amazon Web Services network telemetry covering confirmed threat actor activity from Aug 30 to Aug 31.
Avelogic did not identify affected customers. It said sensitive data fields within SmartHRMS remained protected by application-layer encryption.
The company filed a police report on Aug 31 and notified the Personal Data Protection Commission (PDPC). A PDPC spokesperson told CNA on Wednesday that it was investigating the data breach notification filed.
Avelogic appointed cybersecurity firm Black Panda on Sep 3 to conduct a forensic investigation. It added that it had recovered the latest data set and aimed to have its new system running by Friday.